Making cryptographic guarantees something buyers can act on.
Company
OPAQUE, Series B AI security startup
Role
Product design / discovery lead
Years
2025–2026
The problem
Enterprises want sensitive data in AI, but only if they can prove it’s protected.
What proof has to do:
Unlock the first yes
A builder needs a leave-behind Security can approve, without a lot of follow-up questions.
Keep the yes after go-live
Ongoing proof has to show up where Security already works (SIEM), not in another console.
Be honest about capability
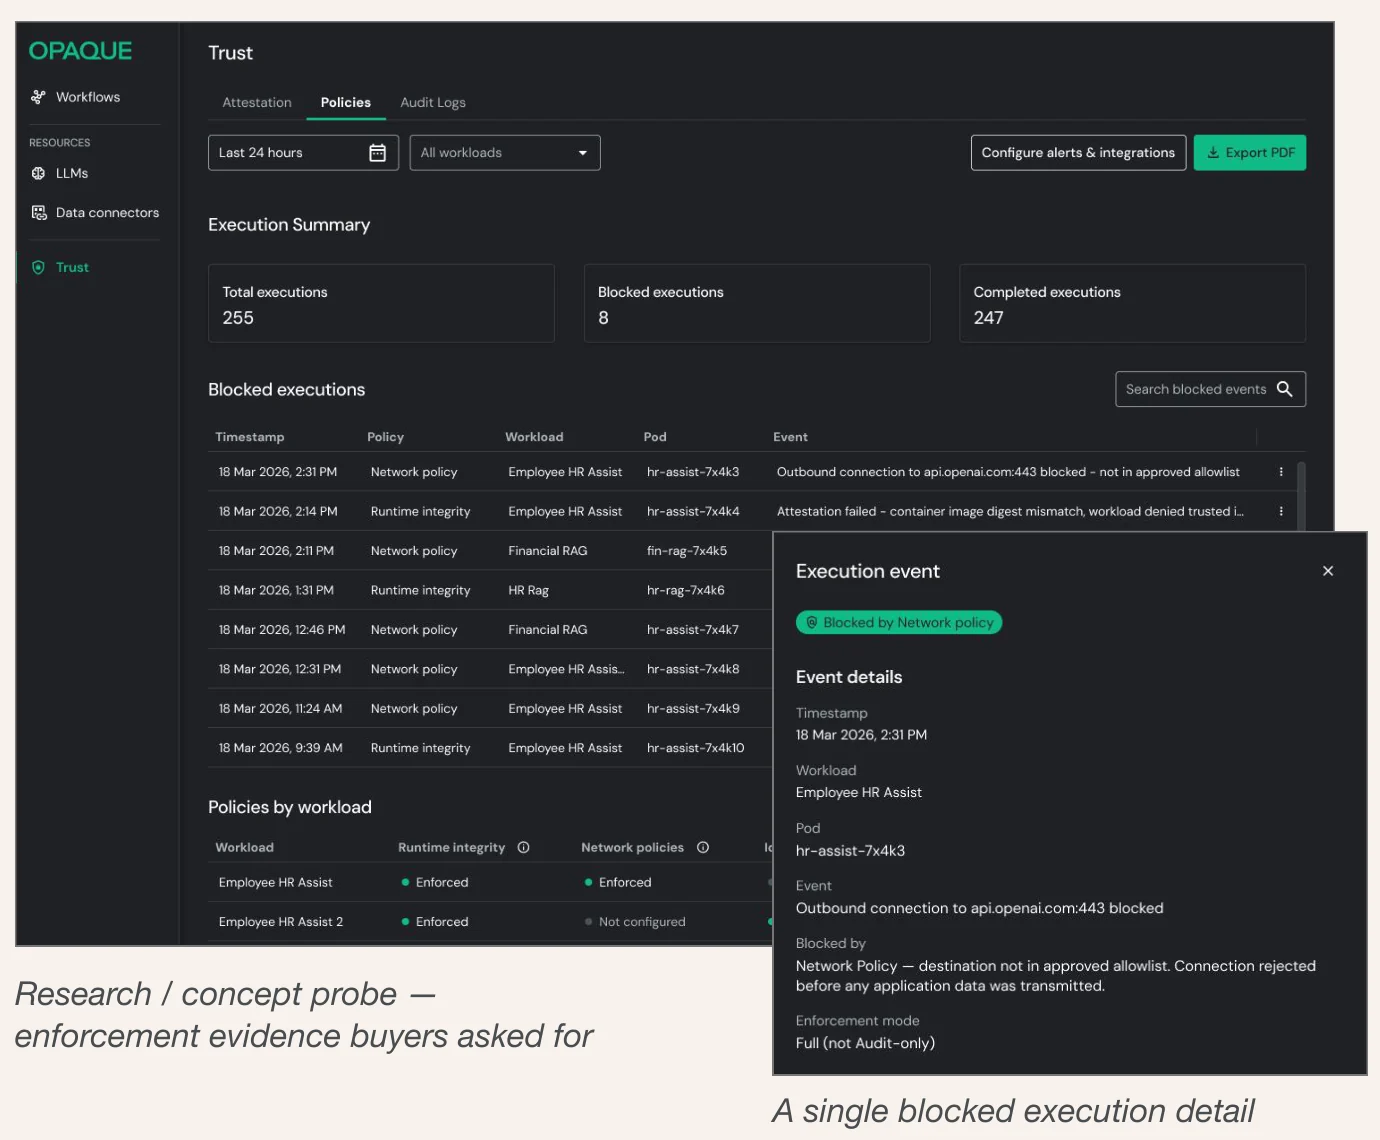
Enforcement evidence resonated, but we couldn’t honestly dashboard it until policy-setting existed.
My first week: “How does the customer know their data is kept safe? What is the artifact we hand to them?”
“I don’t know. Go find out.”
CEO
My role & scope
What I owned
Design
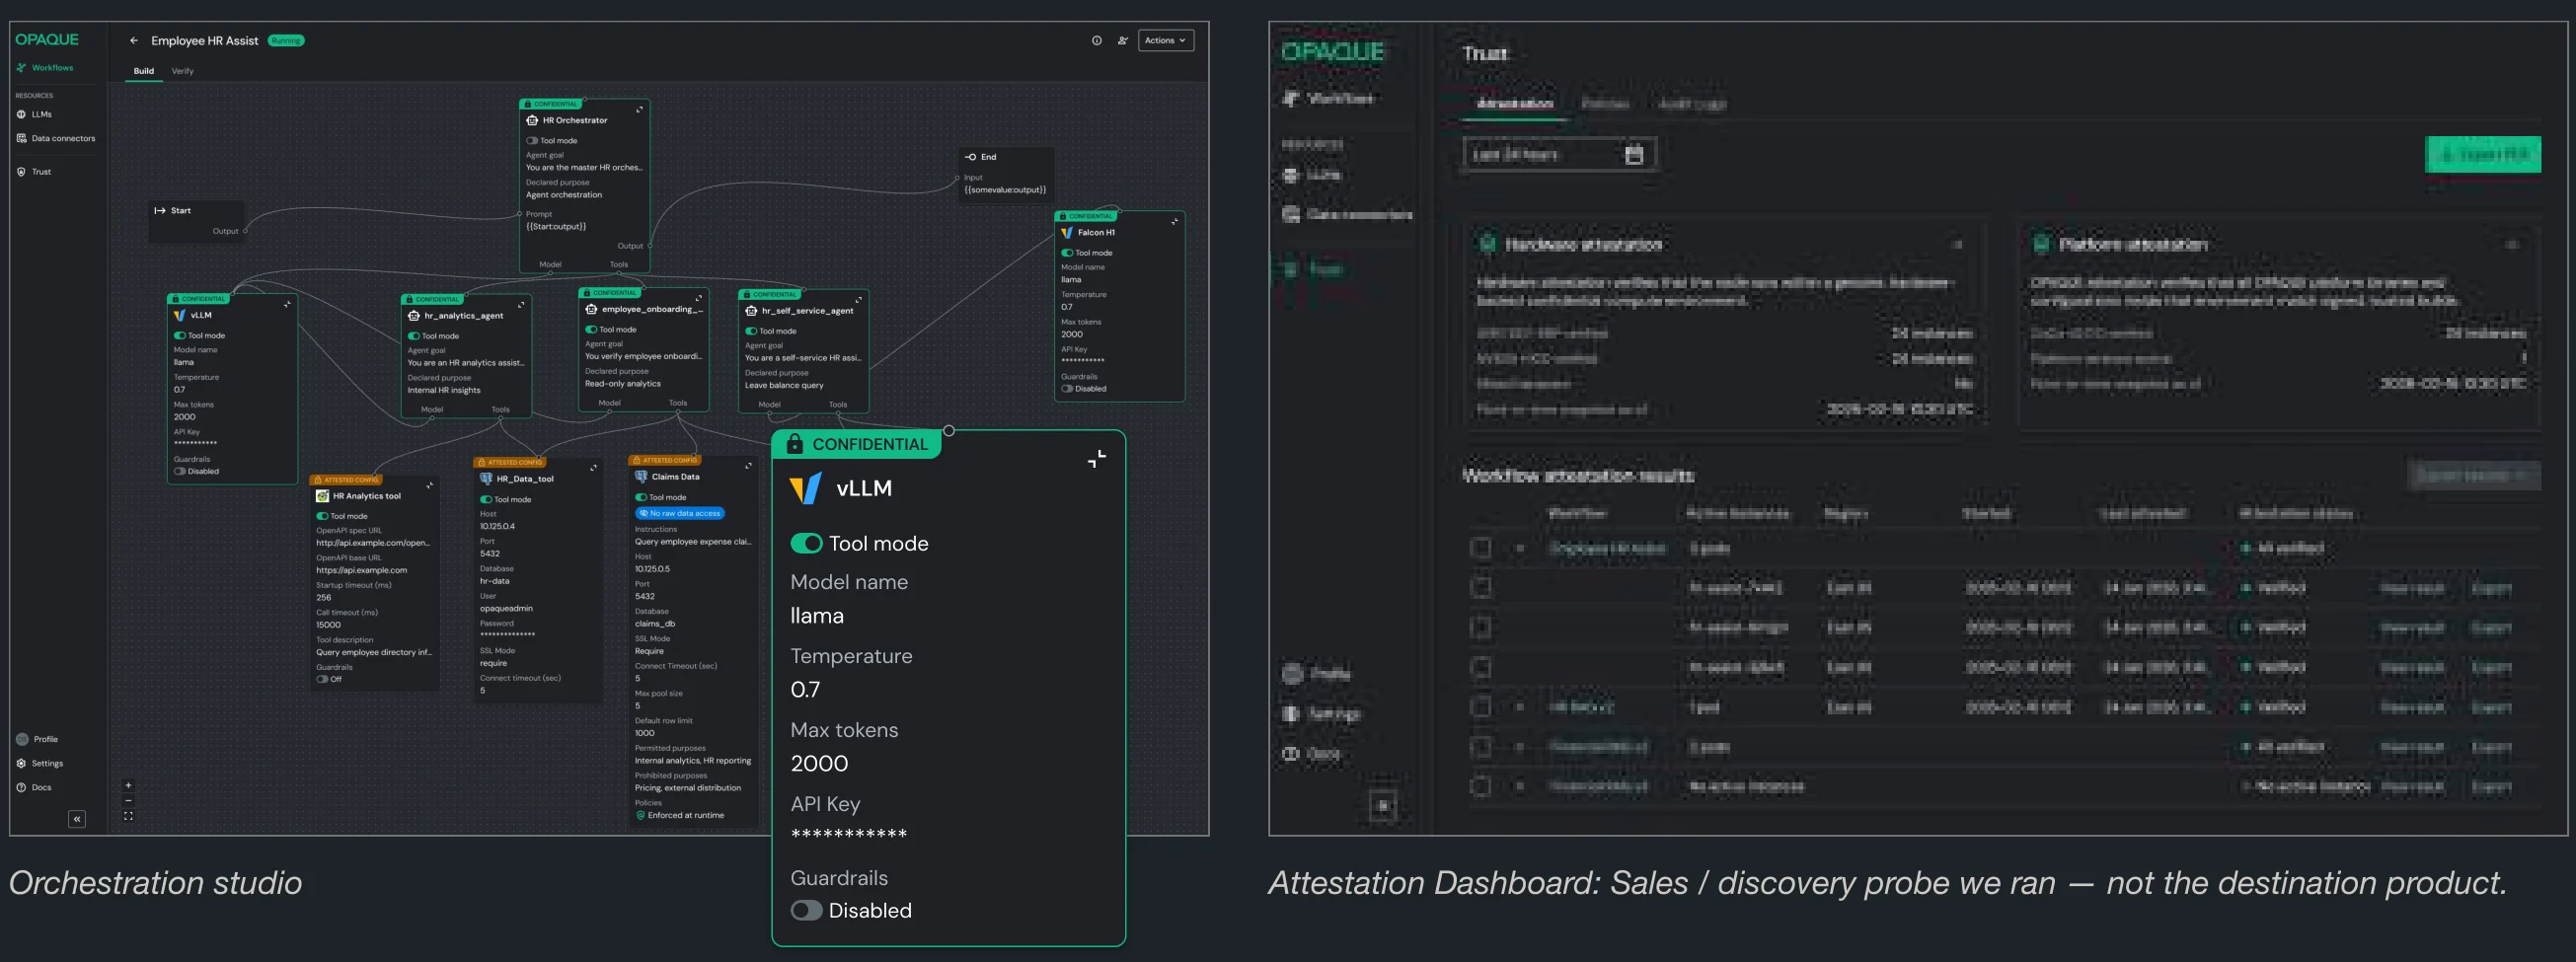
The Attestation Dashboard and reports that made the chain of trust visible, plus a probe that clarified needs we couldn’t fully meet with that surface alone.
Research
Data-leak and resonance synthesis; builder framing; a live attested demo; and validation of a policy-first adoption ladder into the confidential stack (no product marketing).
Product judgment
Recommendations on attestation artifacts and on proof that lands in tools Security already uses.
I partnered with
CEO, CTO and GTM on vision and viability
Engineering on feasibility, cryptography, and platform capabilities
The Product Advisory Council for market validation
Product Management on sequencing and PRDs
Approach
Surface what we could prove, learn what “yes” actually required, change the bet.
Q2 2025Enable GTM
Prototype of orchestration and the Attestation Dashboard, run live in sales calls.
Q4 2025Ship
The proof we could surface: attestation reports prove a workload is running securely.
Q1–Q2 2026Research
Will attested proof clear Security and Legal? Also: which leak stories open the door?
Q2 2026Learn
Policy enforcement engages. Self-verify is high-friction; proof has to export.
Q3 2026Evolve
Paused the Attestation Dashboard; led with evidence primitives.
Q3 2026Position
A policy-first adoption ladder into the confidential stack.
Deep dive: design
UI as discovery, not destiny.
Make the guarantee we had legible. Then adapt.
Deep dive: research
Testing the proof story, and what we learned.
Q1–Q2 2026 · Quant n=150 (leak concern and proof gap) · Qual buy-trigger n=7 · Builders n=6
#1
Policy enforcement is a must-have
Blocked executions mattered more than root-of-trust theater.
“I care less about [hardware root of trust] and I care more about where my policies are stepping in…”Head of Innovation
6/7
Security wants proof in tools they already use
Buy-trigger interviews named SIEM integration independently.
“Why do we need an extra layer like this for the same purpose?”AI Builder, insurance analytics
5/6
Builders wanted a PDF plus regulatory mapping
This packet was the consent packet that would get past legal experts.
“With one report we probably can go ahead with many of the approval from the legal experts.”AI Builder
Pivot
Deprioritize the Attestation Dashboard as a destination
The durable product is evidence primitives that machines and auditors can reuse.
“JSON files [are] crude oil because I can mine it into any how I want it.”AI Builder
Outcome & impact
Proof that moved real enterprises.
Proof validated in market · encryption-in-use as the deal bar · confidential boundary in live workloads
Financial services conglomerate
Southeast Asia
Stage
POC complete; technical validation passed
Use case
Deploy an employee HR chatbot on OPAQUE to add verifiable data protection, then use the validated results as a proof of concept for broader revenue-generating programs.
Proof
An Attested Evidence Pack with third-party verification. The customer ran it, and a cloud partner’s regional chief architect independently validated it.
Signal
A 7+ month POC. Self-verification worked but was high-friction: no local confidential-computing expertise, validation routed through the cloud partner, and later asks included a simpler path.
Credit reporting agency
Global consumer data
Stage
PoV complete; executive readout next
Use case
Consolidate six country instances of a product that resolves identity by matching partner PII against an identity graph into one global instance, while proving the PII is protected during cross-border processing.
Proof
Hardware-signed attestation verified in the PoV; the customer can independently validate the attestation JWT. The PoV bar: governance guarantees before, encryption-in-use during, hardware-signed proof after.
Debt collections company
Consumer credit services
Stage
UAT complete; production cutover next; renewal signed
Use case
Format, compile, and make searchable data across 100+ debt settlement vendors while ensuring consumer PII and SSNs are never exposed as raw data.
Proof
Cryptographic proof that sensitive data (PII) is never decrypted outside the controlled boundary.
Signal
A breach forcing function made confidential guarantees the buy rationale.
“[A sister company] had a situation where their subsidiary was shut down for four months because of a data breach with a third party… we have that same exact use case.”Customer stakeholder
Research pointed to enforcement as the unlock. These accounts show where verifiable protection already moved deals. Enforcement is the next step.
Current state & next steps
Where the proof story stands.
Proof in market · an honest gap · still learning
Now
Confidential Core is in market: the end-to-end confidential stack with hardware-rooted trust (attestation).
Proof work sits on evidence primitives and leave-behinds Security will use; the Attestation Dashboard is no longer treated as the destination surface.
Honest gap: enforcement-quality proof depends on customers being able to set policy and run under it, and that isn’t fully in their hands yet.
Next
Put policy in customers’ hands: set policy, then run under the confidential stack. That turns enforcement into evidence we can honestly show.
Lower the on-ramp: lighter starting points into the confidential stack, so teams can begin without deep confidential-computing expertise.
Keep learning from every customer and prospect at-bat; treat signal as signal, not as PMF confirmation.
Next: Wayfinding, not branding
Testing with 590 users moved a navigation debate from opinion to evidence.